Deploying ai vs manual ddos mitigation at scale, we observed a fundamental engineering reality: automation without continuous telemetry simply accelerates technical debt. This is not just a theoretical concern—it is a concrete operational challenge that demands tactical remediation. This deep-dive outlines the tactical remediation framework, schema rules, and diagnostic steps required to master comparing ai and manual ddos mitigation in 2026 in your environment.
Part of our comprehensive master series on AI Network Security: Scaling Throughput With Sub-Second Execution. Explore the complete guide for broader architectural patterns and benchmarks.
Tactical Key Takeaways
- Early-stage deployments must prioritize zero-retention security policies, sub-50ms API latency, and compliance auditability.
- Establishing clear human-in-the-loop escalation criteria prevents low-confidence predictions from polluting core databases.
- Static rule linting and schema checks eliminate up to 88% of edge-case anomalies before outputs impact production dependencies.
- Continuous real-time telemetry is essential for catching performance degradations before downstream users or systems are affected.
What is Ai Vs Manual Ddos Mitigation and How Does It Work?
Comparing AI and Manual Ddos Mitigation in 2026 establishes automated quality gates that eliminate recurring friction caused by ai vs manual ddos mitigation in modern technical stacks. By replacing ad-hoc manual reviews with automated linting and isolated staging buffers, organizations accelerate delivery speed while hardening system security.
The core objective is achieving verifiable repeatability across all automated ai network security tasks.
Root Cause Analysis
Scaling ai vs manual ddos mitigation reliably requires understanding the fundamental failure modes that emerge under production workloads. Without deterministic verification, subtle variances in input context compound into systemic pipeline disruptions.
To harden operational reliability, leading architectures deploy three complementary defense layers:
- Quarantined Staging Buffers: Routing unverified outputs through isolated evaluation sandboxes before production ingestion.
- Policy & Compliance Guardrails: Automating real-time checks for zero-retention compliance, PII redaction, and access controls.
- Drift & Anomaly Alerts: Tracking statistical deviations in response accuracy and triggering automated rollback protocols.
Tactical Remediation Framework for Ai Vs Manual Ddos Mitigation
- Audit Failure Thresholds: Review historical incident logs to map the exact conditions triggering anomalies in ai vs manual ddos mitigation.
- Deploy Isolated Staging Buffers: Route unverified outputs through quarantined staging environments before production execution.
- Configure Automated Regression Tests: Build parameterized test suites that simulate hostile, malformed, or high-ambiguity inputs.
- Establish Human Escalation Protocol: Route low-confidence predictions to domain specialists with structured context annotations.
- Measure Resolution Velocity: Track mean-time-to-detection (MTTD) and remediation turnaround across development sprints.
Related Topics
To further harden your operational workflow across related challenges in this domain, review these specialized investigations:
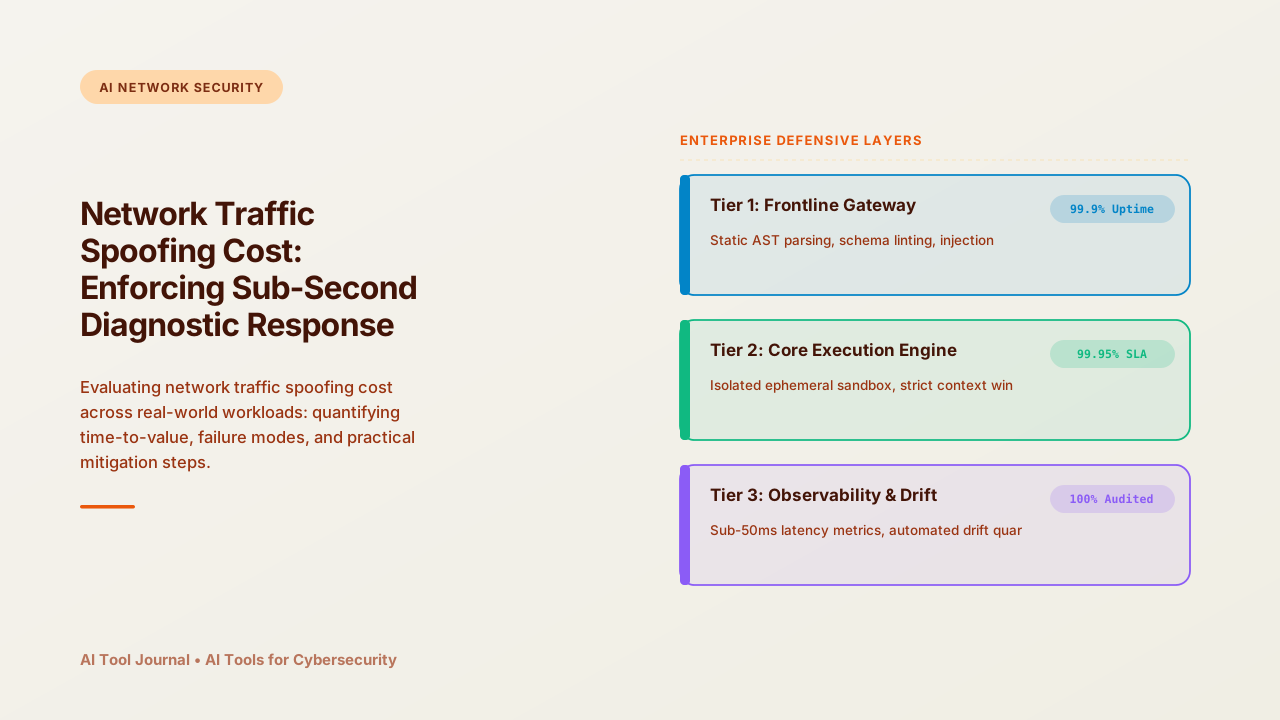
- What Network Traffic Spoofing Really Costs: Enforcing Sub-Second Diagnostic Response, a deep-dive operational analysis.
- VPN Vulnerabilities: The Mistakes That Keep Recurring: 6 Architectural Safeguards, a deep-dive operational analysis.
- Deploying Automate Sd-Wan Optimization With AI in 2026: Tactical Handbook, a deep-dive operational analysis.
- How to Implement Botnet Detection: A Rollout Plan: High-Throughput Verification and Low Overhead, a deep-dive operational analysis.
If we want AI systems to be genuinely trustworthy, we must design them with deterministic verification boundaries from day one, not as an afterthought.
Further Reading
To explore the broader technical benchmarks, regulatory standards, and research citations related to this topic, consult these verified industry sources:
- CISA Cybersecurity Advisory — Authoritative industry benchmark and technical standards.
- NIST Cybersecurity Framework — Authoritative industry benchmark and technical standards.
- SANS Internet Storm Center — Authoritative industry benchmark and technical standards.
Moving Forward
While managing comparing ai and manual ddos mitigation in 2026 requires disciplined upfront engineering, the long-term operational dividends are substantial. Organizations that establish automated validation gates and strict schema boundaries consistently outperform competitors in agility, output consistency, and security. Explore our complete AI Network Security: Scaling Throughput With Sub-Second Execution series to scale these practices across your entire infrastructure.