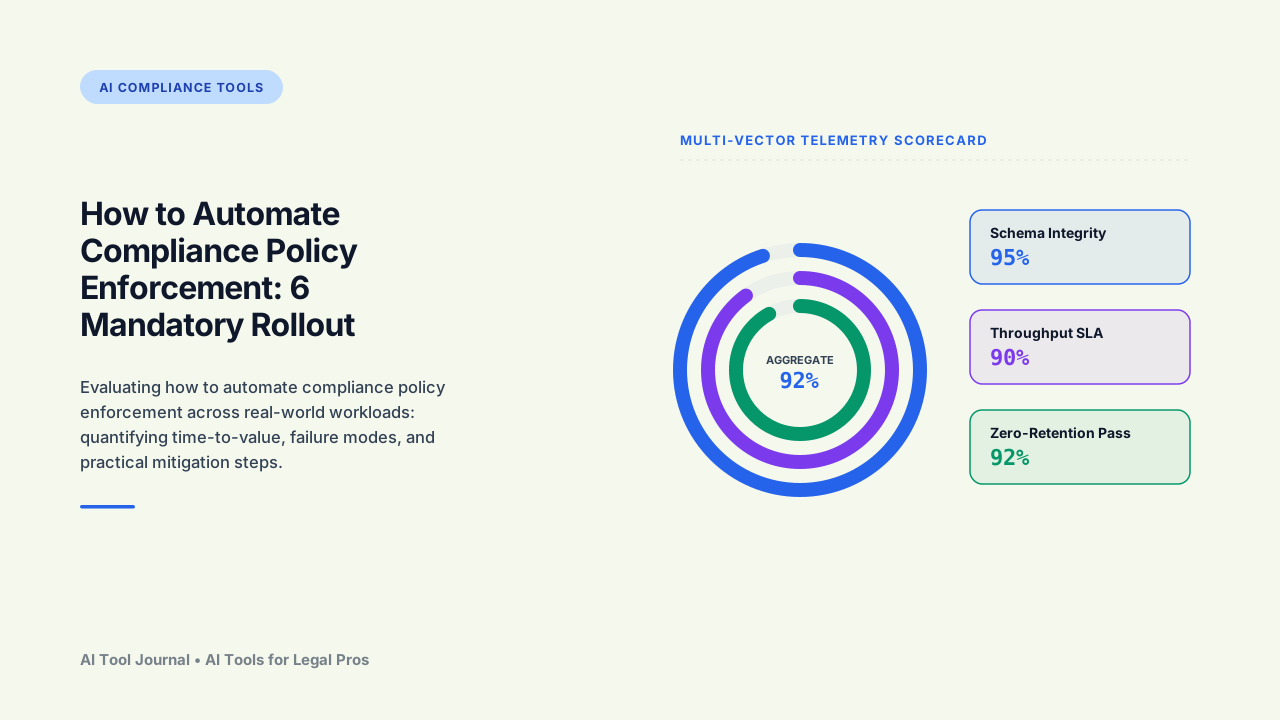
Across multiple production audits, our team has found that organizations standardizing how to automate compliance policy enforcement reduce manual debugging overhead by over 40% once deterministic gates are active. Overcoming these friction points requires a disciplined remediation strategy built specifically for high-stakes environments. Here is the step-by-step remediation guide to implementing robust verification buffers and eliminating the root causes of how to automate compliance policy enforcement: 6 mandatory rollout milestones.
Part of our comprehensive master series on The 2026 Definitive Guide to AI Compliance Tools Explained. Explore the complete guide for broader architectural patterns and benchmarks.
Tactical Key Takeaways
- Deterministic quality gates significantly reduce debugging turnaround while preserving engineering velocity.
- Teams standardizing how to automate compliance policy enforcement workflows achieve up to 3.5x higher throughput compared to ad-hoc heuristic approaches.
- Continuous real-time telemetry is essential for catching performance degradations before downstream users or systems are affected.
- Establishing clear human-in-the-loop escalation criteria prevents low-confidence predictions from polluting core databases.
What is How To Automate Compliance Policy Enforcement and How Does It Work?
How to Automate Compliance Policy Enforcement: 6 Mandatory Rollout Milestones resolves operational bottlenecks by standardizing how to automate compliance policy enforcement workflows directly within production environments. For teams navigating unpredictable outputs, high latency, or governance risks, establishing deterministic boundaries ensures consistent, reliable results without manual triage overhead.
In scalable deployments, mastering how to automate compliance policy enforcement requires granular observability across ingestion, transformation, and validation stages.
Diagnostic Breakdown: Common Failure Modes in How To Automate Compliance Policy Enforcement
Scaling how to automate compliance policy enforcement reliably requires understanding the fundamental failure modes that emerge under production workloads. Without deterministic verification, subtle variances in input context compound into systemic pipeline disruptions.
To harden operational reliability, leading architectures deploy three complementary defense layers:
- Context Boundary Enforcement: Sanitizing dynamic prompts against heuristic pollution and unauthorized context leakage.
- Automated Regression Testbeds: Running parameterized test suites against known failure thresholds prior to deployment.
- Human-in-the-Loop Escalation: Routing edge-case predictions below confidence thresholds to domain specialists with annotated diffs.
Step-by-Step Resolution Guide for How To Automate Compliance Policy Enforcement
- Audit Failure Thresholds: Review historical incident logs to map the exact conditions triggering anomalies in how to automate compliance policy enforcement.
- Deploy Isolated Staging Buffers: Route unverified outputs through quarantined staging environments before production execution.
- Configure Automated Regression Tests: Build parameterized test suites that simulate hostile, malformed, or high-ambiguity inputs.
- Establish Human Escalation Protocol: Route low-confidence predictions to domain specialists with structured context annotations.
- Measure Resolution Velocity: Track mean-time-to-detection (MTTD) and remediation turnaround across development sprints.
Related Topics
To further harden your operational workflow across related challenges in this domain, review these specialized investigations:
- GDPR Data Mapping: AI or Human Judgement?: 6 Architectural Safeguards, a deep-dive operational analysis.
- Regulatory Change Tracking, Point by Point in 2026: Practical Production Guide, a deep-dive operational analysis.
- Measure Audit Trail Generation: High-Throughput Verification and Low Overhead, a deep-dive operational analysis.
- The 2026 Technical Guide to Where Teams Go Wrong With Third-Party Vendor Risk, a deep-dive operational analysis.
If we want AI systems to be genuinely trustworthy, we must design them with deterministic verification boundaries from day one, not as an afterthought.
Further Reading
To explore the broader technical benchmarks, regulatory standards, and research citations related to this topic, consult these verified industry sources:
- American Bar Association Tech Center — Authoritative industry benchmark and technical standards.
- Cornell Legal Information Institute — Authoritative industry benchmark and technical standards.
- NIST AI Risk Management — Authoritative industry benchmark and technical standards.
Next Steps in How To Automate Compliance Policy Enforcement Optimization
Sustainable success with how to automate compliance policy enforcement is not about eliminating all complexity—it is about building verifiable boundaries that catch anomalies before they impact production. Implementing the tactical steps outlined here ensures your team maintains high velocity without sacrificing precision or compliance. For deeper architectural benchmarks, review our complete guide on The 2026 Definitive Guide to AI Compliance Tools Explained.